Event Platform API
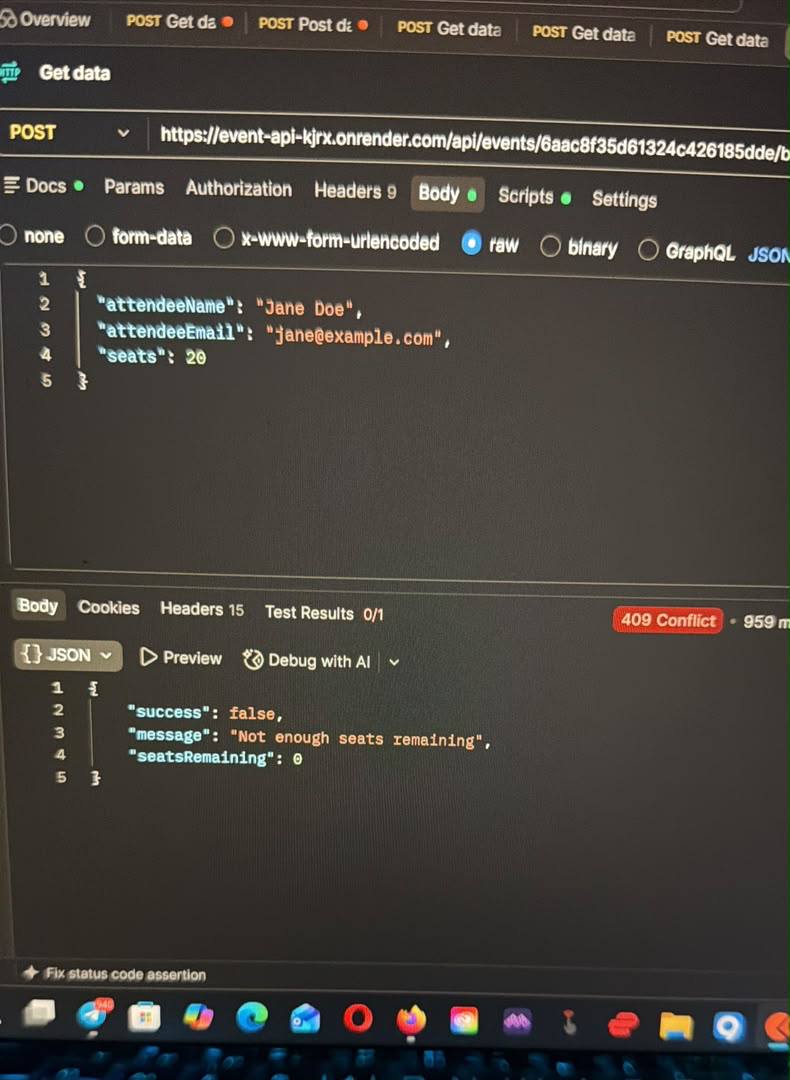
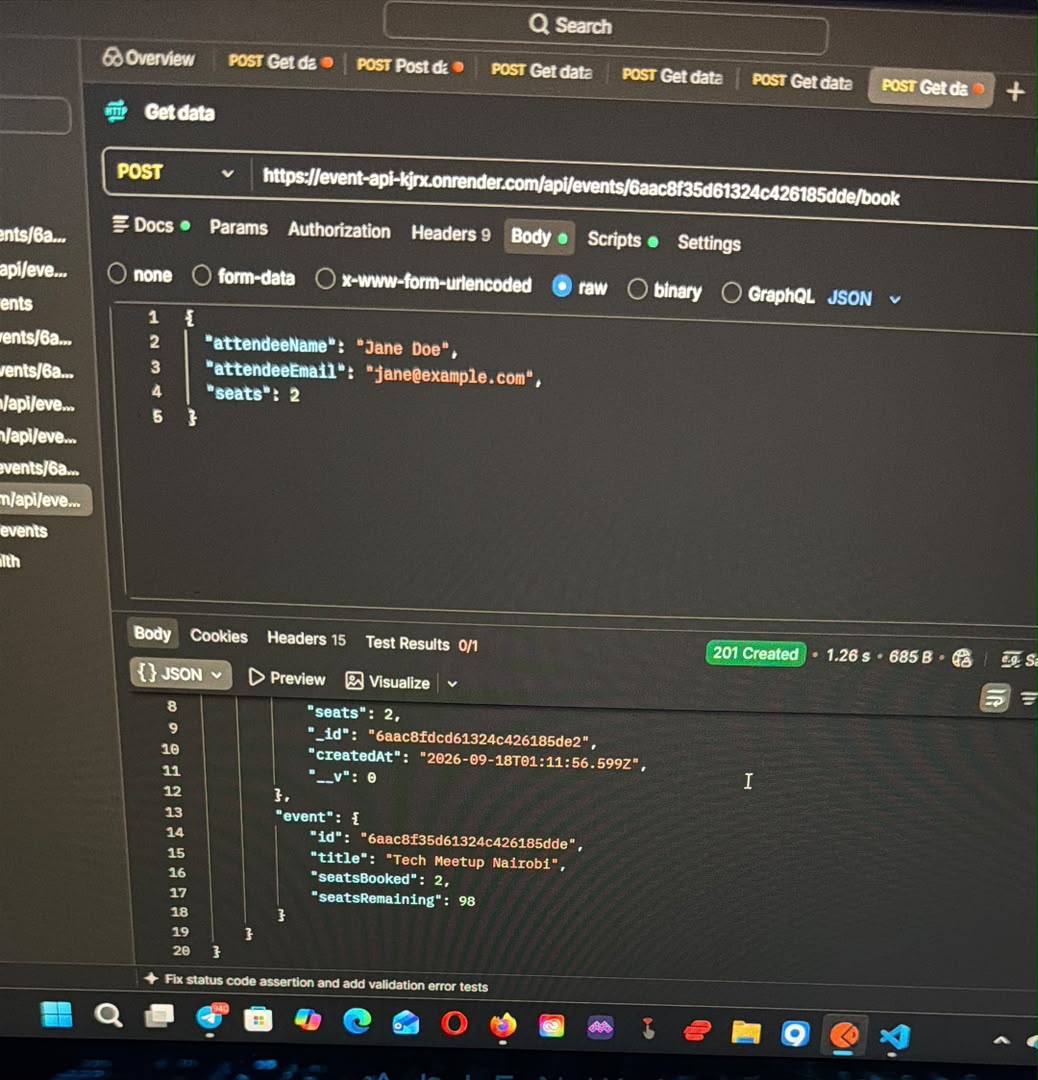
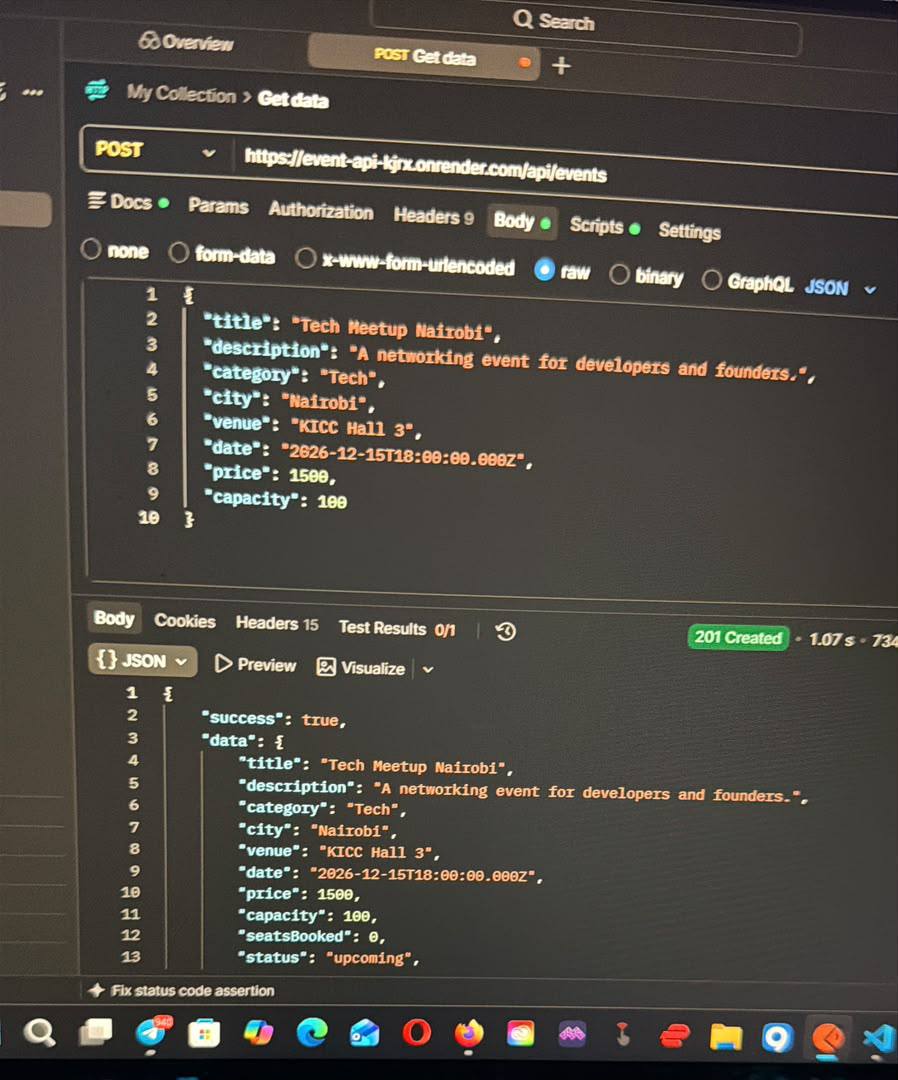
An event platform API that creates, updates, deletes and lists events, and can fetch any event by its ID. Increments are handled atomically. My best one yet.
Digital creator / problem solver
I build thoughtful digital experiences with a sharp eye for detail and a curious mind for what comes next.
Explore the workSelected work
An event platform API that creates, updates, deletes and lists events, and can fetch any event by its ID. Increments are handled atomically. My best one yet.
Built in the company of amazing tech fellows at Bethechified.
For experiments, collaborations or case studies, head to my GitHub.
Capabilities
Reliable endpoints for creating, updating, listing, and connecting the data your product needs.
Clear, responsive interfaces that make complex products feel simple to use.
Integrations and automations that move information where it needs to go.
Live API / attack it yourself
A defensive API for websites and apps. It does two jobs: quarantine bad data before it reaches your database (SQL injection, XSS, path traversal, log4shell, obfuscated payloads, even encoded evasions), and stop abuse before it reaches your users (brute force, credential stuffing, password spraying, distributed attacks) with bans that escalate on repeat offenders. It runs entirely in your browser and speaks real HTTP semantics. Fire the recipes, launch a simulated attack, edit anything, or open devtools and call xeno.fetch('/v1/quarantine'). Prefer a terminal? Test both with curl →
| Captured data | Threat | Review | Hits |
|---|
| Subject | State | Blocked |
|---|
Live API / insurance claims
How an insurer actually handles a claim, as an API. File a claim and the engine checks the policy (active, in force, waiting period, coverage, exclusions, filing window), works out what would be payable after the deductible, coinsurance and remaining limit, scores it for fraud with every red flag spelled out, then routes it: straight-through approval, an adjuster, special investigations, or automatic denial. Adjusters decide and pay; claimants edit, appeal and withdraw. I built it because I study insurance and write backends, and this is where the two meet. Click a claim to see why it was routed the way it was, or run a scenario. Run it with curl instead →
| Claim | Amount | Fraud risk | Status |
|---|
| Policyholder | Status | Cover used |
|---|
Test it with curl
Both APIs also run as a real HTTP server you start on your own machine. Clone the repo, run one command, and hit them with curl. The PDF guide walks through 46 commands for both APIs, and every one was executed against the live server, so the results it shows are real.
1. Get the code
git clone https://github.com/Roodie77/jonathan-portfolio.git
cd jonathan-portfolio
2. Start the server
node server.js --fresh
3. In a second terminal, load the helpers and make your first call
source scripts/curl-helpers.sh
api $INS
The server listens on localhost only, so nothing is exposed to the internet. On Windows use Git Bash or WSL.
428), a wrong role (403), a stale read (412)200 200 429 429 403 403…